By Greg Nowak. Updated 7 November 2026.
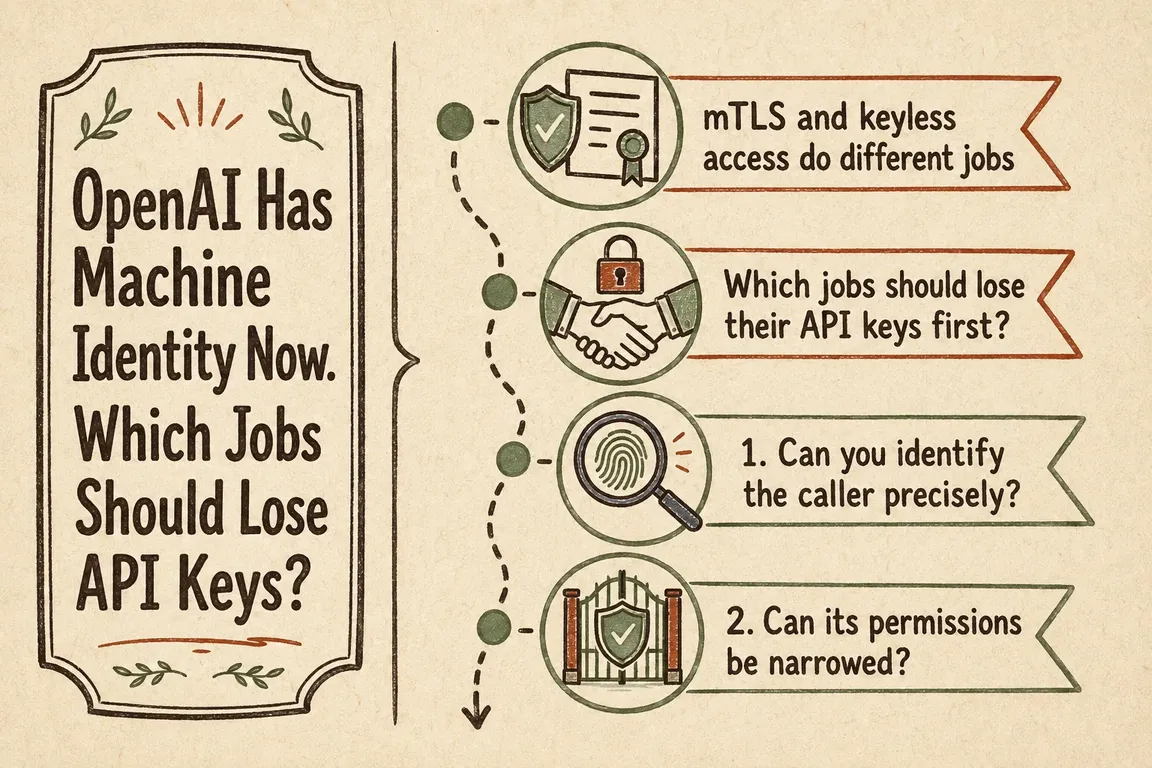
The first OpenAI jobs I would move away from API keys are unattended workflows with a named owner, an existing machine identity, and a straightforward recovery path. A scheduled reporting job or a well-controlled CI workflow can be a sensible pilot. A shared credential used by several poorly documented integrations needs an inventory first.
For business owners, the benefit is fewer long-lived OpenAI secrets to distribute and retire. For operations and agency teams, the trade-off is maintaining the identity system that replaces them. The migration should make access easier to explain, restrict, and recover when something breaks.
What changes when you replace an API key?
OpenAI workload identity federation exchanges a trusted workload identity for a short-lived OpenAI access token mapped to a project service account. OIDC uses an external identity token; X.509 uses a verified client certificate.
Mutual TLS (mTLS) adds client-certificate verification alongside the bearer credential. Enabling mTLS on an API-key integration therefore keeps the key. X.509 federation replaces that key with a short-lived token, while API requests still require an accepted certificate.
My recommendation is to start with the identity your infrastructure already manages reliably. Adding certificate infrastructure solely to remove one API key may create more maintenance than it saves.
Which jobs should move first?
| Current situation | Suggested next step | Readiness check |
|---|---|---|
| CI or cloud job with a documented OIDC integration | Pilot OIDC federation | Exact issuer, audience, and workload mapping; reliable token retrieval. |
| Server job with automated certificate management | Evaluate X.509 federation | Protected private key, automatic renewal, and stable certificate identity. |
| Job needs certificate verification while retaining its bearer credential | Evaluate mTLS | Every affected caller supports certificates and the required host. |
| Unrelated jobs share one key | Separate ownership and access first | Identify each consumer, project, permission set, and failure contact. |
| Vendor connector accepts only an API key | Keep a restricted key pending vendor support | Secure storage, rotation owner, and a date to review support. |
A reporting job is useful when a failed run can be detected and safely repeated. A customer-facing workflow may justify migration sooner, but needs stronger availability testing. For agencies, keep each client's access and handover separately accountable, with distinct production and test identities.
Make the identity mapping specific
For GitHub Actions federation, grant the job id-token: write and request the exact audience configured in OpenAI. This permission allows OIDC-token issuance; it does not grant repository write access. Restrict the mapping to the intended repository and branch or deployment environment. Review mappings when repositories move or change names.
For other OIDC environments, check OpenAI's documented provider configurations before committing to a design. An OIDC-compatible issuer is not automatically a supported OpenAI API integration; contact OpenAI if yours is unlisted.
Set explicit mapping permissions. Blank permissions add no federation-specific scope restriction: access follows the mapped service account's roles. A shorter credential lifetime does not reduce what the workload is allowed to do.
What an X.509 implementation involves
The X.509 setup guide describes the configuration and SDK examples. The essential sequence is:
- Upload and activate certificate trust under Organization settings > Security > Mutual TLS, initially for a non-critical project.
- Create an X.509 provider under Security > Workload Identity Provider. Derive a non-empty
openai.subjectfrom a stable certificate attribute and map its exact value to the intended service account. - Give the runtime its certificate chain, private key, provider ID, and service account ID. Present the leaf certificate followed by required intermediates; OpenAI does not retrieve missing intermediates.
- Exchange the certificate at
POST https://mtls.auth.openai.com/oauth/token. Callhttps://mtls.api.openai.com/v1with the returned bearer token and an accepted client certificate.
Check SDK version requirements before implementation. Supported SDK configurations handle token renewal, but certificate renewal still needs an operational owner.
Test renewal and recovery before retiring keys
The token exchange reference specifies a maximum one-hour lifetime, bounded by the external token or certificate's expiry. There is no refresh token. Manual implementations must repeat the exchange before expires_at, allowing for clock differences and network delays.
- Inventory all callers. Include monthly scripts, temporary deployments, and vendor connectors. Record owners, endpoints, permissions, and the consequence of failure.
- Contain the pilot. Uploading trust does not enforce mTLS; activation changes request behaviour. Test every affected caller before expanding its scope.
- Exercise failures. Test expired identities, missing intermediates, rejected mappings, and temporary exchange failures. Confirm alerts reach someone able to act.
- Prove recovery. Document who can restore configuration, pause jobs, and resume unfinished work without duplicate processing. An old API key alone cannot bypass active mTLS requirements.
- Retire credentials deliberately. Rotate trust anchors with overlap, move callers, then deactivate old trust. Revoke replaced API keys after confirming scheduled and occasional consumers have migrated.
Know which credentials must remain
OpenAI's documented token limitations exclude Admin APIs, DELETE /v1/models/{id}, and POST /v1/images/request_audit. Admin automation still needs an admin API key. Private Link is incompatible with mTLS, so check the network design before choosing X.509.
X.509 bearer tokens are not cryptographically bound to their certificates, and OpenAI does not perform CRL or OCSP revocation checks. Protect tokens and private keys, keep them out of logs, and plan incident response around trust, provider, and mapping controls, including already-issued tokens.
If your team needs a starting point, discuss an OpenAI authentication review with Greg. I can help inventory callers, choose a pilot, agree acceptance checks with your developers, and document the handover so someone clearly owns renewal and recovery.
Related on GrN.dk
- Your AI Workflow Runs on One Person’s API Key. Now What?
- AI automations need a spend dashboard before the first runaway bill
- Cloudflare Service Keys Stop in September: Find Every Caller
Need help with this kind of work?
Discuss an OpenAI authentication review with Greg Get in touch with Greg.