Before your AI agent starts clicking, write a browser policy
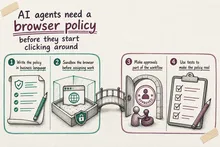
A practical browser-agent policy for safer access, approvals, prompt-injection controls, audit evidence and rollout across live business systems.
A practical browser-agent policy for safer access, approvals, prompt-injection controls, audit evidence and rollout across live business systems.
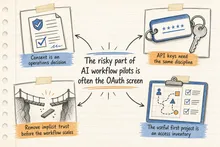
Before clicking Allow on an AI workflow pilot, check its permissions, data access, ownership, spending limits and shutdown plan with this practical checklist.
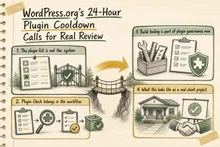
WordPress.org’s plugin cooldown adds a useful safety buffer, but businesses still need a practical process for testing, approving, and reversing updates.
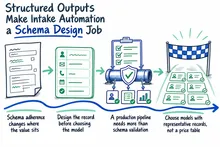
Structured Outputs reduce format failures, but reliable intake automation still depends on schema design, validation, model choice, and controlled handoffs.
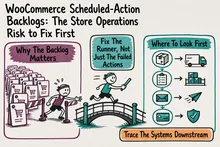
A practical guide to WooCommerce scheduled-action backlogs, what they break in store operations, and how to audit WP-Cron, WP-CLI runners, renewals, and webhooks.
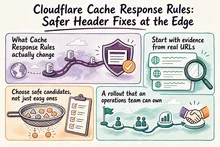
Cloudflare Cache Response Rules can fix cache-blocking headers on public pages. Learn how to diagnose BYPASS, scope a safe rule, and verify the result.
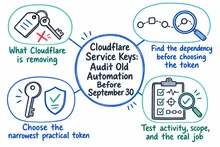
Cloudflare Service Keys stop working September 30, 2026. Find legacy scripts, choose scoped API tokens, test the cutover, and document ownership.
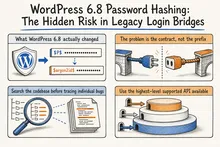
WordPress 6.8 changed password hashing quietly. Learn how to find brittle login bridges, use supported APIs, and test legacy accounts before they fail.
Learn when to replace WordPress WP-Cron with server cron, choose a sensible interval, and migrate safely with commands and checks for critical business tasks.
Flush Ubuntu’s DNS cache, identify the resolver your application uses, and verify website, email or API changes before calling a migration complete.
Written recommendations from Trafik og Veje, Aarhus Municipality (2011) and AgroTech (2010).
