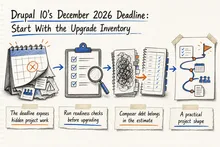
Drupal 10 reaches end of life on December 9, 2026. Use this practical inventory to scope Drupal 11 readiness, Composer debt, modules, and custom code.
Recent content
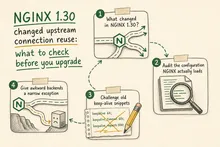
NGINX 1.30 reuses HTTP backend connections by default. Audit inherited settings, test older applications, and roll out with clear monitoring and a rollback path.
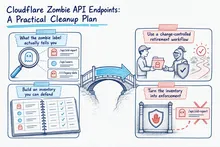
Cloudflare’s zombie API label flags inactivity, not safe deletion. Follow a practical cleanup process with ownership checks, staged removal and rollback planning.
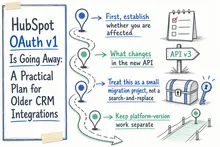
HubSpot OAuth v1 retires on February 16, 2027. Find legacy calls, update token handling, test existing connections, and give the rollout a clear owner.
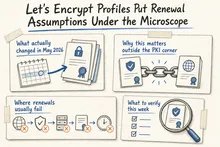
Let’s Encrypt profiles expose weak renewal processes. Learn what changed, what comes next, and how to test Certbot, challenges, hooks, and monitoring.
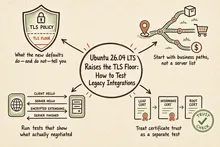
Upgrading to Ubuntu 26.04 LTS? Test legacy TLS integrations, certificate trust and real business workflows before cutover, with a clear rollback plan.
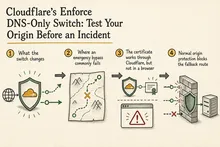
Cloudflare’s account-wide DNS-only switch can bypass its proxy in an emergency. Test certificates, firewalls, capacity, and rollback before relying on it.
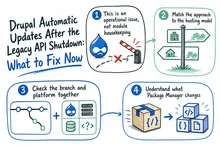
Still relying on Drupal’s retired update API? Check module compatibility, Composer and hosting requirements, then build a tested update process with clear ownership.
Review an inherited Apache reverse proxy: verify security fixes, map business-critical routes, and plan an upgrade with practical checks and clear ownership.
Cloudflare Tunnel is easier to inspect in 2026. Review ownership, routes, access, failover and logging so your team can support the services behind it.
Cloudflare Cache Response Rules can fix cache-blocking headers on public pages. Learn how to diagnose BYPASS, scope a safe rule, and verify the result.
Cloudflare Service Keys stop working September 30, 2026. Find legacy scripts, choose scoped API tokens, test the cutover, and document ownership.
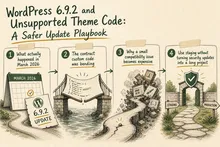
WordPress 6.9.2 exposed unsupported theme-loading code. Learn how to audit template hooks, stage security updates, and reduce emergency troubleshooting.
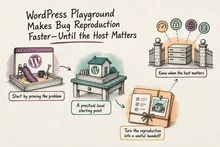
WordPress Playground can turn a vague bug report into a repeatable test. Learn when to use the browser, CLI, Blueprints, Docker, or host staging.
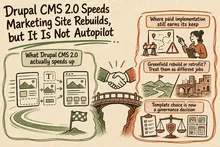
Drupal CMS 2.0 can cut first-build time for marketing site rebuilds with Canvas, templates, and recipes, but theme fit, permissions, integrations, and governance still shape launch risk.
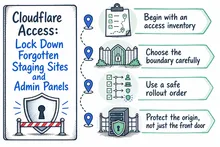
A practical guide to finding exposed staging sites and admin panels, protecting them with Cloudflare Access, and handling origins and automation safely.
WordPress 6.8 changed password hashing quietly. Learn how to find brittle login bridges, use supported APIs, and test legacy accounts before they fail.
A practical HPOS migration plan for established WooCommerce stores: audit dependencies, rehearse the cutover, verify order data, and prepare rollback.
A practical post-launch SEO checklist using Search Console hourly data, URL Inspection and release logs to investigate problems and protect valuable landing pages.
Understand WordPress’s autoloaded options warning, identify oversized settings, and plan a safe cleanup that protects checkout, admin workflows, and future updates.
Written recommendations from Trafik og Veje, Aarhus Municipality (2011) and AgroTech (2010).
