By Greg Nowak. Updated 3 November 2026.
A forgotten API route can leave old functionality exposed. Removing it too quickly can break a supplier integration, a quarterly report or a customer’s older application. Cloudflare’s zombie label helps you find routes worth investigating; the retirement decision needs more evidence.
For business owners, operations leads and agency teams, the useful outcome is a smaller API surface with clear ownership, documented dependencies and a controlled removal plan. Here is how to get there.
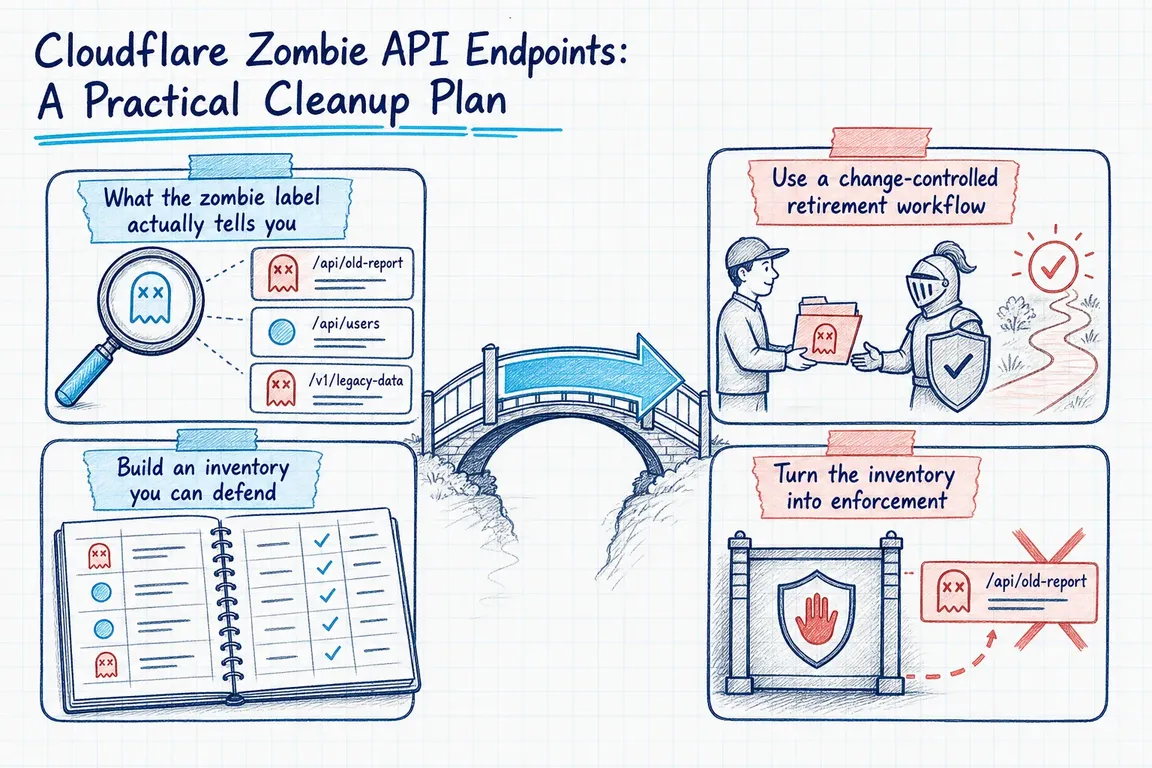
What does Cloudflare’s zombie API label mean?
Cloudflare automatically applies cf-risk-zombie when a saved endpoint has received no traffic for 32 days. Risk scans run approximately once a day, according to its endpoint labeling documentation.
That is a reason to investigate. Monthly processes can slip outside the window; quarterly integrations, seasonal services and recovery tools may legitimately remain quiet for longer. Check whether Cloudflare can observe every relevant route into the service, too.
Deleting an operation in Cloudflare does not remove its application handler. Cloudflare also warns that deleting a full operation stops its associated analytics tracking and permanently loses its historical metrics. Preserve the evidence before cleaning the dashboard.
Build an evidence trail before choosing a retirement date
Start in Web Assets > Operations. Record each operation by HTTP method, hostname and normalized path. For example, GET api.example.com/users/{userId} and DELETE api.example.com/users/{userId} need separate decisions. Cloudflare’s Endpoint Management documentation explains operation identity and deletion behavior.
Compare the inventory with gateway and origin logs, deployed routes and the current OpenAPI document. Search repositories, scheduled jobs, integration records and support tickets. An old mobile client or supplier script may still depend on a route that current application code no longer calls.
Do not treat absence from Discovery as proof of inactivity. Cloudflare’s Discovery requirements include at least 500 qualifying sampled requests within a continuous 10-day period, returning 2xx at the edge. Requests originating directly from Workers, including Worker-based test harnesses, do not count. Quiet or failing integrations can therefore be missing.
| What you find | What it tells you | Next step |
|---|---|---|
| Zombie label alone | Cloudflare observed an inactive saved endpoint. | Check consumers and other traffic records. |
| No traffic, but a scheduled business dependency | The route may still be required. | Retain it with an owner and review date. |
| No traffic and no identified owner | Ownership is unresolved. | Escalate the decision and assess exposure. |
| Confirmed obsolete; dependencies resolved | Retirement can be scheduled. | Approve removal, monitoring and rollback. |
| Application removal verified | The capability has been retired. | Archive evidence and clean Cloudflare inventory. |
Give the technical and business decisions named owners
The service owner confirms how the route works, where it is deployed and how to reverse the change. The business owner checks customer commitments, supplier dependencies and internal processes. In an agency arrangement, record which client representative accepts the business impact and which delivery lead owns implementation.
For every candidate, keep one ticket containing its purpose, environment, authentication, data sensitivity, known consumers, evidence period and proposed outcome. Use clear states: required, awaiting investigation, deprecation planned or approved for removal.
Unknown ownership should trigger investigation and proportionate containment. OWASP identifies missing inventories and retirement strategies as contributors to exposed, unpatched APIs in API9:2023 Improper Inventory Management. Leaving an unexplained route open indefinitely needs an accountable decision, too.
Retire the route through a controlled release
- Choose a meaningful evidence window. Cover the business cycle the endpoint supports. If logs do not extend far enough, record that limitation and seek confirmation from consumers rather than calling the route unused.
- Agree what happens to remaining callers. Provide a replacement endpoint and deadline where needed. Define the expected error after retirement and tell support how to recognize affected integrations. Keep authentication, authorization and rate controls active during deprecation.
- Prepare the release and rollback. Identify the application, gateway or Worker that serves the capability. Save the relevant configuration, assign the person who can reverse the release and agree which failed requests or business symptoms would trigger that response.
- Remove the capability at its source. Disable or remove the handler through the normal deployment process. Update the OpenAPI document, integration guidance and relevant tests alongside it. Verify that the retired functionality cannot still be reached through another hostname or deployment.
- Monitor before closing the change. Watch requests to the retired path, application errors, scheduled jobs and support reports. An expected rejection may reveal a missed consumer without requiring immediate rollback; investigate its identity and business impact.
- Clean Cloudflare last. Once removal is verified, archive the decision and traffic evidence. Check rules referencing the operation before deleting it, then give any remaining exception an owner and review date.
Keep inventory cleanup separate from enforcement changes
A cleanup release is easier to assess when broad blocking changes have their own review. Cloudflare’s Schema Validation documentation describes detection through cf.schema_validation.uploaded.violated; mitigation requires a separate WAF custom rule. Review representative traffic before enforcing it.
Dashboard schema uploads add operations automatically; API and Terraform workflows require separate operation creation. Validation uses OpenAPI 3.0 semantics. Compatible 3.1 uploads can succeed, but 3.1-only semantics are unsupported. Uploading a replacement schema also leaves validation definitions for omitted operations active, so review old definitions explicitly.
For fallthrough rules, cf.api_gateway.fallthrough_detected matches requests outside saved operations, including requests matching candidate operations. Scope enforcement to the intended API hostname or root path and investigate legitimate matches before blocking.
Make the next cleanup easier
Add ownership and retirement checks to release reviews. For an agency handover, leave the client an inventory, a decision log and a clear list of unresolved dependencies. Those records make the next change easier to approve.
If your team has zombie labels but no agreed way to act on them, Greg can help review the inventory and turn the findings into a practical retirement plan, with responsibilities, rollout steps and rollback decisions agreed before implementation.
Related on GrN.dk
- Cloudflare Service Keys Stop in September: Find Every Caller
- Cloudflare Page Rules Debt: How Old Rules Break Business Websites
- Cloudflare Service Keys: Audit Old Automation Before September 30
Need help with this kind of work?
Plan a safe API cleanup with Greg Get in touch with Greg.