Join my community / free newsletter — sign up here
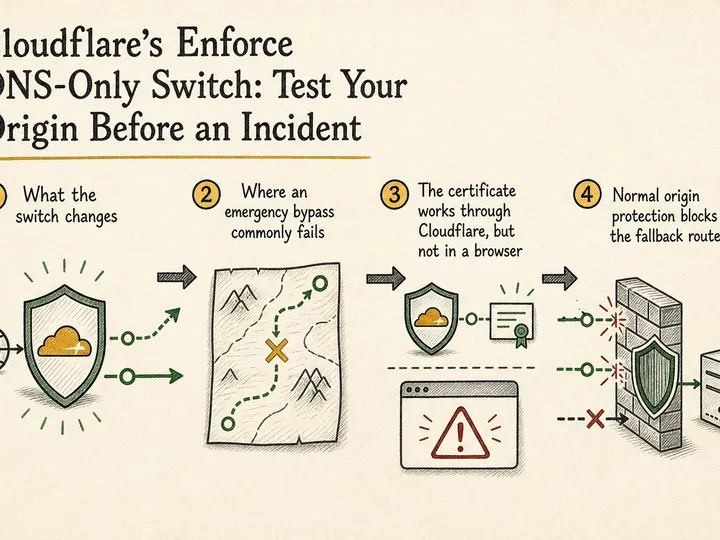
Cloudflare’s account-wide DNS-only switch can bypass its proxy in an emergency. Test certificates, firewalls, capacity, and rollback before relying on it.
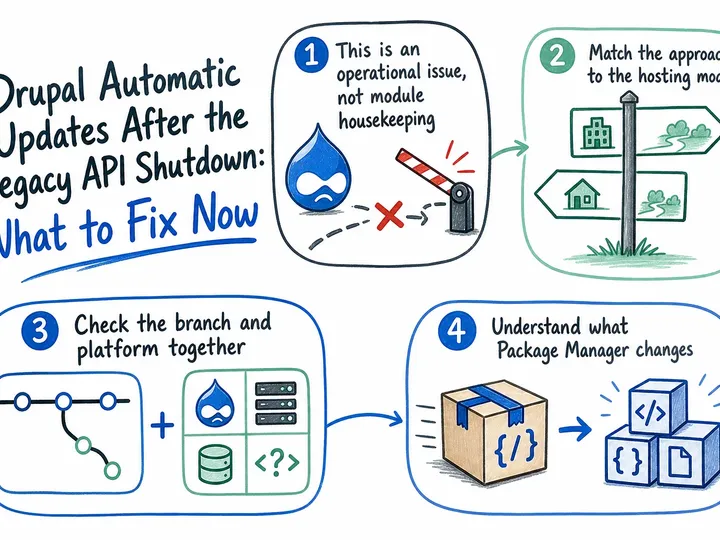
The legacy Drupal update API is gone. Choose a supported update path, check Composer and hosting constraints, and rehearse safer Drupal releases.
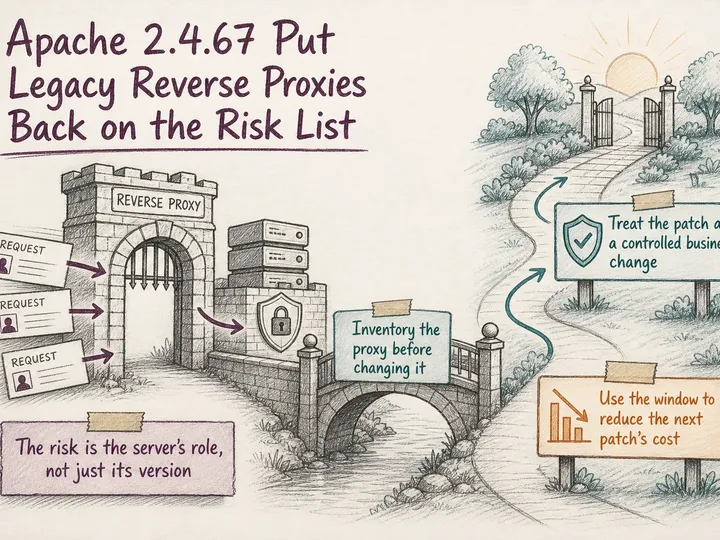
Apache 2.4.67 put inherited reverse proxies back in focus. Learn how to verify vendor fixes, map exposed routes, and upgrade without losing critical traffic.
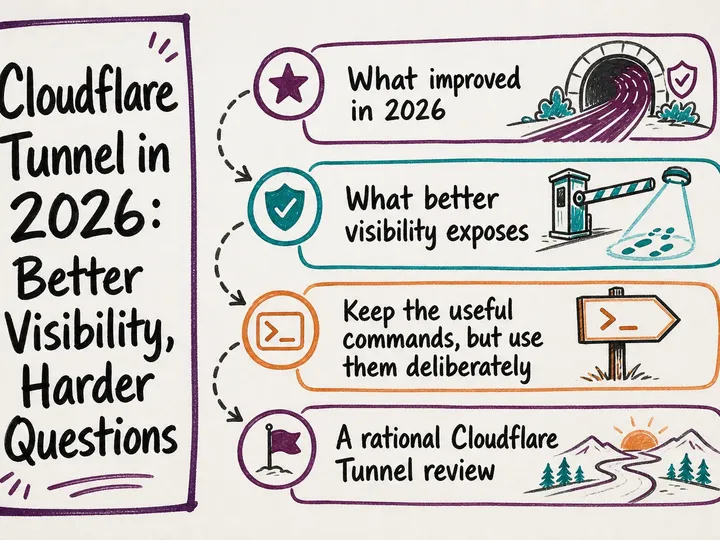
Cloudflare Tunnel is easier to inspect in 2026. Review ownership, routes, access, failover and logging so your team can support the services behind it.
Cloudflare Cache Response Rules can fix cache-blocking headers on public pages. Learn how to diagnose BYPASS, scope a safe rule, and verify the result.
Cloudflare Service Keys stop working September 30, 2026. Find legacy scripts, choose scoped API tokens, test the cutover, and document ownership.
WordPress 6.9.2 exposed unsupported theme-loading code. Learn how to audit template hooks, stage security updates, and reduce emergency troubleshooting.
WordPress Playground can turn a vague bug report into a repeatable test. Learn when to use the browser, CLI, Blueprints, Docker, or host staging.
Drupal CMS 2.0 can cut first-build time for marketing site rebuilds with Canvas, templates, and recipes, but theme fit, permissions, integrations, and governance still shape launch risk.
A practical guide to finding exposed staging sites and admin panels, protecting them with Cloudflare Access, and handling origins and automation safely.
WordPress 6.8 changed password hashing quietly. Learn how to find brittle login bridges, use supported APIs, and test legacy accounts before they fail.
A practical HPOS migration plan for established WooCommerce stores: audit dependencies, rehearse the cutover, verify order data, and prepare rollback.
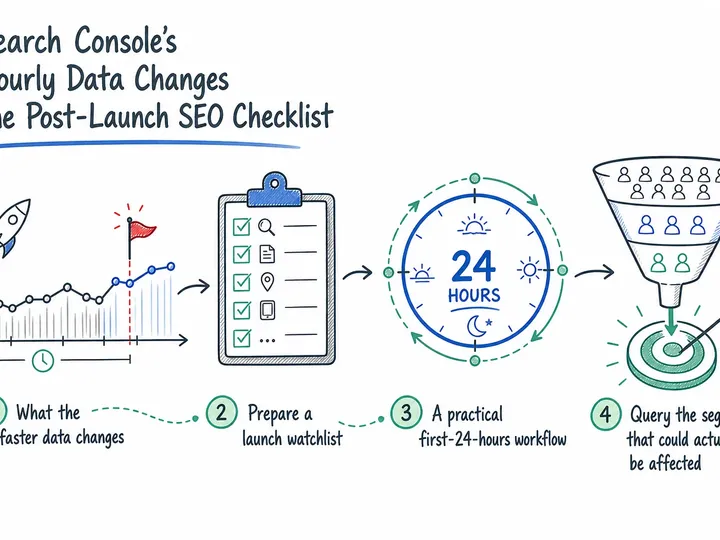
A practical post-launch SEO checklist using Search Console hourly data, URL Inspection and release logs to investigate problems and protect valuable landing pages.
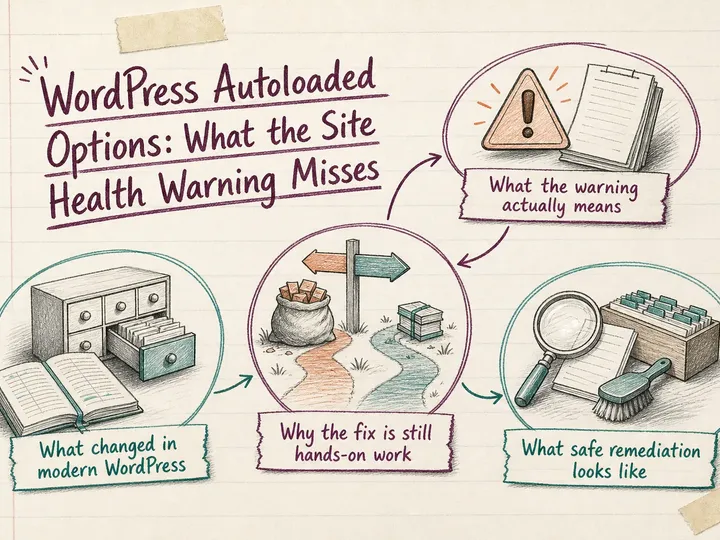
WordPress Site Health can flag bloated autoloaded options, but safe fixes depend on tracing oversized or stale data, save logic, and request-path impact.
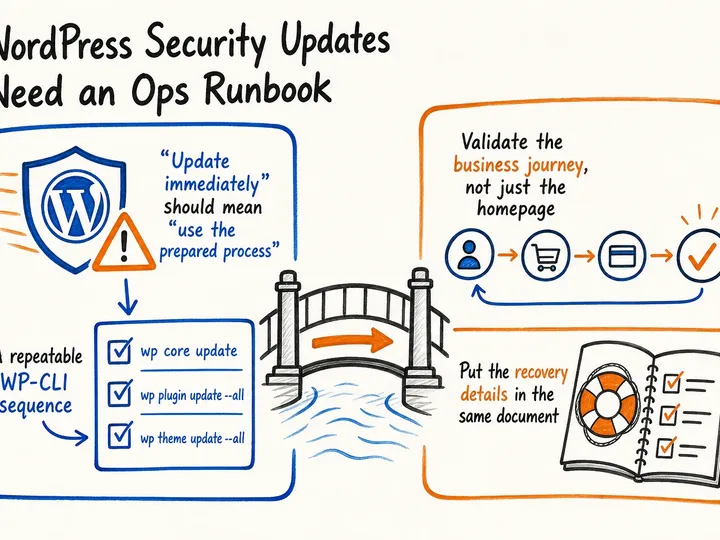
A practical WordPress security update runbook covering backups, WP-CLI execution, database changes, validation, recovery, and clear ownership.
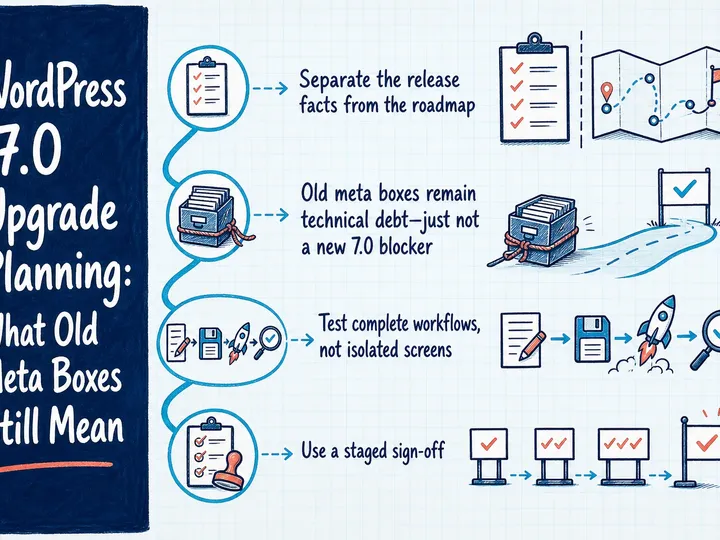
Plan your WordPress 7.0 upgrade with practical checks for old meta boxes, hosting compatibility, publishing workflows, staging tests, and safe rollback.
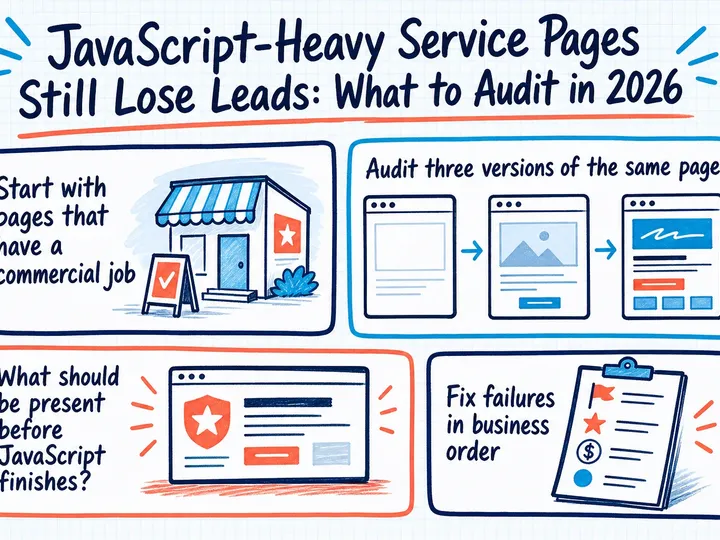
A practical 2026 audit for service pages that rely on JavaScript, covering initial HTML, mobile parity, status codes, responsiveness, and lead paths.
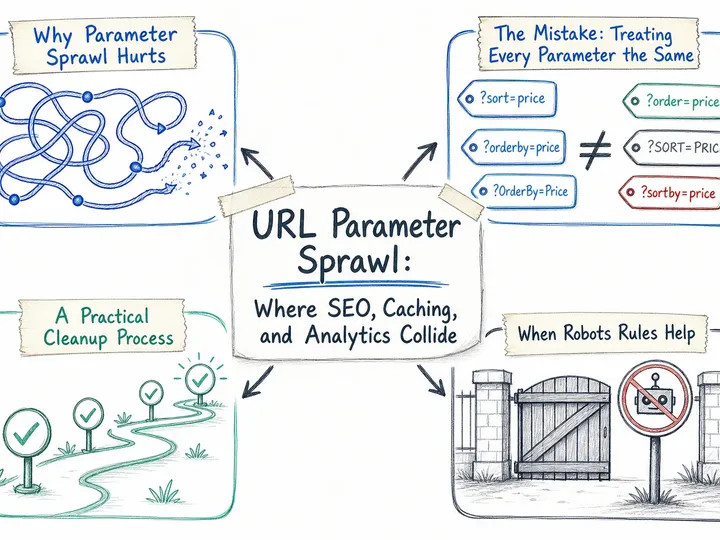
Bring URL parameters under control with a practical policy for search, Cloudflare caching, and analytics—without breaking filters or losing campaign attribution.
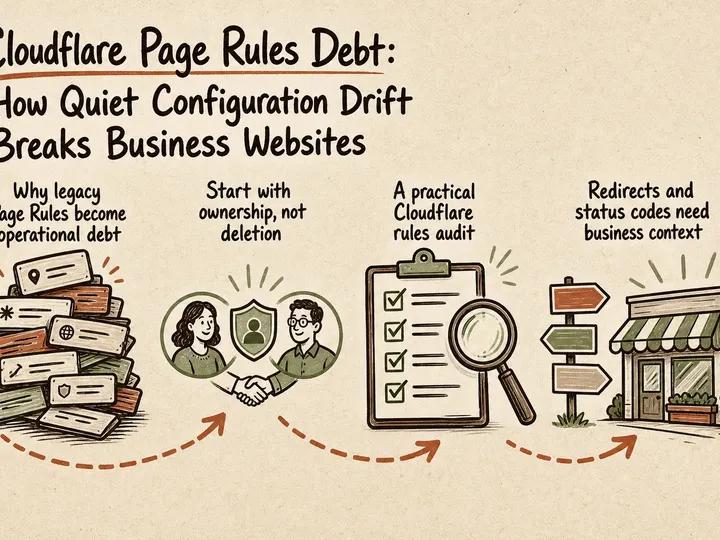
Cloudflare rules debt can quietly disrupt redirects, caching, forms, and SEO. Learn how to audit critical request paths and clean up overlapping rules.
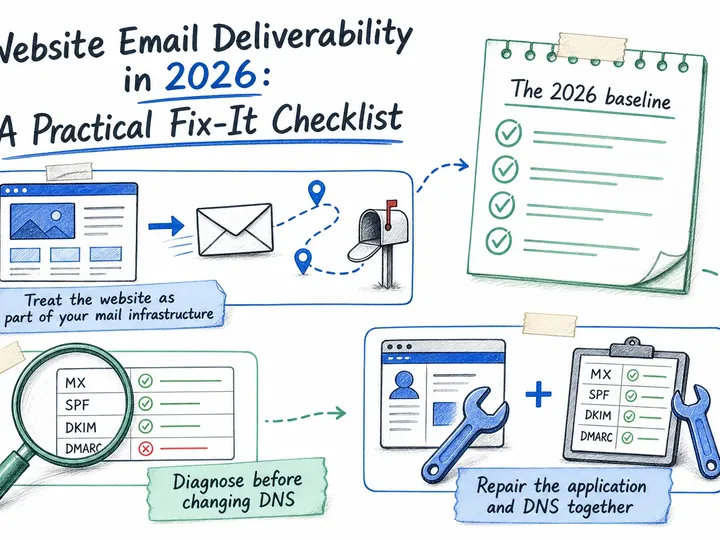
Missing website enquiries, receipts or password resets? Trace failed mail, check SPF, DKIM and DMARC, and give your team a clear plan to restore reliable delivery.
Review Greg on Google
5.0 ★★★★★ 10 Google reviews
Written recommendations from Trafik og Veje, Aarhus Municipality (2011) and AgroTech (2010).