WordPress supply-chain attack: why the CDN key changed the response
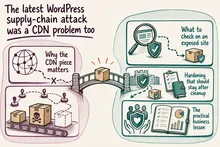
A practical response to the June 2026 WordPress CDN supply-chain attack: who was exposed, what to check, and how to prevent another compromise.
A practical response to the June 2026 WordPress CDN supply-chain attack: who was exposed, what to check, and how to prevent another compromise.
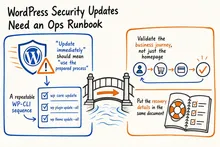
A practical WordPress security update runbook covering backups, WP-CLI execution, database changes, validation, recovery, and clear ownership.

A practical 2026 audit for service pages that rely on JavaScript, covering initial HTML, mobile parity, status codes, responsiveness, and lead paths.

Inherited Cloudflare rules can disrupt forms, redirects, caching, and SEO. Learn what to audit, how to migrate safely, and what a useful handover should include.

Missing website enquiries, receipts or password resets? Trace the failure, check SPF, DKIM and DMARC, and give your team a practical plan for reliable delivery.

Third-party scripts affect speed, data, resilience, and conversion. Learn how to assign ownership, audit the stack, and govern every vendor dependency.

Reduce form spam without losing genuine enquiries. A practical guide to server checks, targeted rate limits, field validation, and cleaner CRM routing.

A practical guide to choosing a supported PHP version, finding CMS compatibility blockers, testing critical workflows and planning a reversible upgrade.
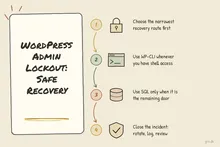
Recover WordPress admin access safely with WP-CLI, careful database fallbacks, and a practical process that helps prevent the next lockout.

WordPress invalid JSON errors usually point beyond the editor. Follow a safe diagnostic path through REST requests, redirects, firewalls, plugins, and PHP.
Written recommendations from Trafik og Veje, Aarhus Municipality (2011) and AgroTech (2010).
