Shorter TLS Certificates: Will Your Renewal Setup Keep Up?
Shorter TLS certificates leave less room for renewal problems. Check domain validation, scheduling, deployment and the certificate your customers actually receive.
Shorter TLS certificates leave less room for renewal problems. Check domain validation, scheduling, deployment and the certificate your customers actually receive.
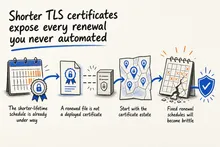
Shorter TLS lifetimes make certificate renewal a frequent production workflow. Learn how to automate validation, deployment, verification, and alerts.
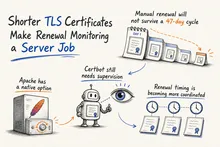
Public TLS lifetimes are moving from 200 days toward 47. Manual renewal is now a reliability risk across ACME, reloads, monitoring, and rollback.
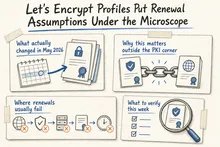
Let’s Encrypt profiles expose weak renewal processes. Learn what changed, what comes next, and how to test Certbot, challenges, hooks, and monitoring.
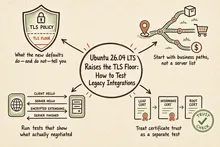
Ubuntu 26.04 LTS retires legacy TLS defaults. Learn how to inventory dependencies, test certificates and stage a rollback-ready upgrade.
Written recommendations from Trafik og Veje, Aarhus Municipality (2011) and AgroTech (2010).
