By Greg Nowak. Last updated 2026-07-14.
Ubuntu 26.04 LTS gives Apache and Nginx a more sensible security baseline. It also creates a useful deadline for dealing with integrations that still depend on obsolete TLS.
Canonical lists Apache 2.4.66 and Nginx 1.28.2 in the release. Apache disables TLS 1.0 and 1.1 by default, while Nginx defaults to TLS 1.2 and 1.3. That follows the direction set by RFC 8996, which formally deprecated TLS 1.0 and 1.1.
The security decision is straightforward. The operational work is not. A forgotten webhook, warehouse device, reporting script or partner API can turn a routine server upgrade into a business interruption. The answer is a small compatibility project with named owners, observable tests and a credible rollback path.
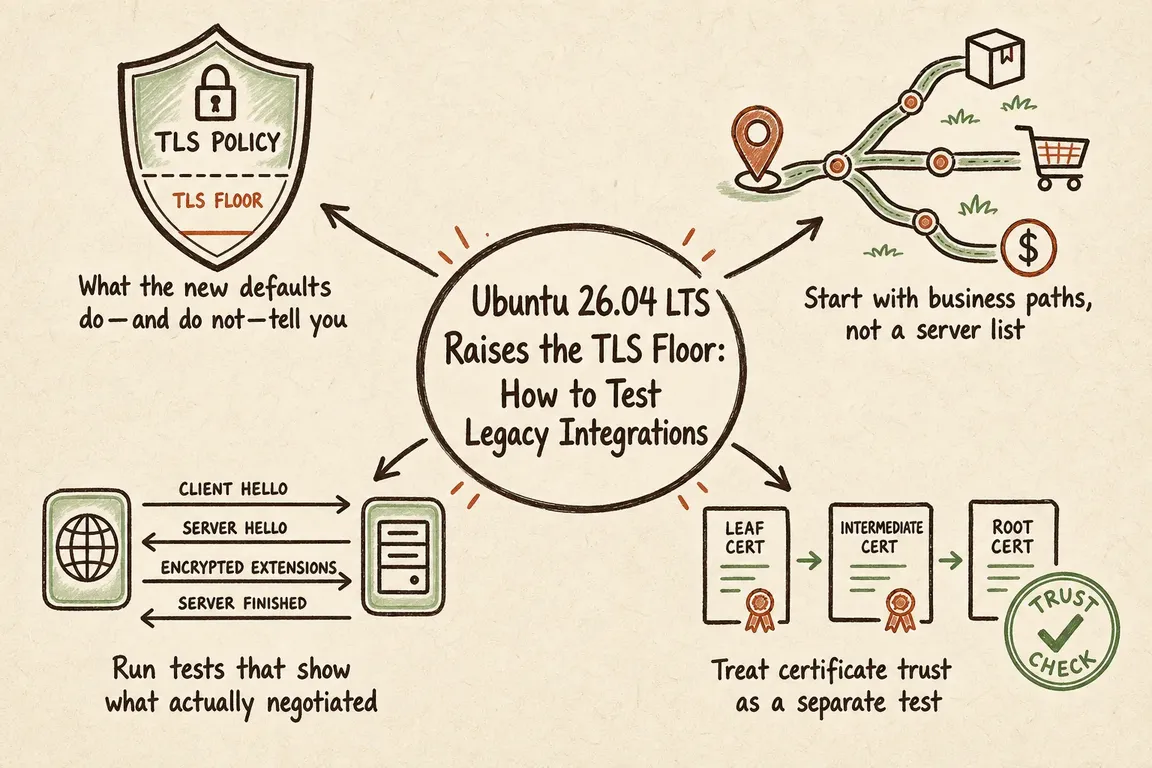
What the new defaults do—and do not—tell you
Ubuntu’s packaged defaults describe the expected baseline for newly configured services. They do not prove that every upgraded server will behave identically. Explicit Apache or Nginx directives, copied virtual-host files, reverse proxies and configuration-management templates can all preserve different settings.
Audit the effective configuration, not just the package version. More importantly, remember that TLS has two sides. Your web server may be ready while an old client is not, or an outbound application on the upgraded host may reject a partner’s incomplete certificate chain.
| Connection path | Evidence to collect | Likely problem | Business owner |
|---|---|---|---|
| Public sites and portals | Negotiated TLS version, full certificate chain, redirects and proxy path | Old browser, scanner or monitoring client | Hosting or operations |
| Partner APIs and webhooks | Successful request and callback from a representative runtime | Legacy vendor endpoint or stale trust store | Operations plus vendor contact |
| Jobs and internal services | Completed batch run, service logs and expected output | Old language runtime, pinned library or private CA | Engineering or IT |
| Devices and appliances | Real connection from production-equivalent firmware | Client cannot negotiate TLS 1.2 or validate the chain | IT, facilities or supplier |
Start with business paths, not a server list
Build the inventory around work the organisation must keep running: customer logins, payment notifications, order feeds, file transfers, scheduled reports, monitoring and remote devices. For each path, record the client, server, DNS name, proxy or CDN, certificate issuer, runtime owner and vendor contact.
Then classify each path by impact and control. A public brochure site is usually easy to test and roll back. A webhook from a vendor you cannot simulate needs earlier coordination. An embedded device with fixed firmware may require replacement rather than another configuration tweak.
Define the pass condition before testing. “The page opened” is weak evidence. “The job completed from the upgraded runtime, the certificate validated, the expected record arrived and monitoring stayed green” is much more useful.
Run tests that show what actually negotiated
Canonical’s current troubleshooting guidance recommends separating the client and server during diagnosis. OpenSSL configuration is read by both sides, so testing both roles on one specially configured machine can hide the source of a failure.
These commands provide a quick starting point. Including -servername makes the first test work correctly with servers that select certificates using SNI:
echo | openssl s_client -connect api.example.com:443 \
  -servername api.example.com 2>&1 | grep '^New'

sslscan api.example.com:443
The first command reports the negotiated TLS version and cipher. sslscan inventories the protocols and ciphers exposed by the endpoint. Keep the output with the rollout record so the team has evidence rather than a collection of screenshots and recollections.
Do not stop at the public homepage. Run outbound requests from the Ubuntu 26.04 staging host, trigger inbound webhooks, execute scheduled jobs and exercise mutual-TLS connections. Where possible, test with the actual application runtime and a production-equivalent certificate.
Treat certificate trust as a separate test
A failed TLS connection is not automatically a protocol-version problem. Common causes include a missing intermediate certificate, a hostname mismatch, an expired certificate or a private issuer that the client does not trust.
For internet-facing services, use a publicly trusted CA and configure the server with the complete chain. For private services, distribute the organisation’s CA certificate into the relevant client trust stores. Ubuntu’s documentation recommends considering an internal CA when a network has more than a few self-signed certificates; that is generally easier to govern than maintaining one-off trust exceptions.
Stage the rollout and make rollback specific
Move a representative low-risk host first, then a higher-risk integration group, and only then the remaining estate. After each stage, check application logs, failed handshakes, webhook queues, job completion and business outputs.
A rollback plan should name the exact trigger, decision owner and action. It might restore the previous instance, switch traffic back through the load balancer or revert a deployment image. “We can reinstall if necessary” is not a rollback plan.
If one critical dependency genuinely cannot support TLS 1.2, avoid weakening the public baseline for everything. Prefer a narrowly scoped, monitored and time-limited exception with an owner and retirement date. Use that window to upgrade the client, replace the device or move the supplier.
Turn the upgrade into an orderly project
The difficult part is rarely typing the TLS directive. It is finding hidden dependencies, obtaining a realistic vendor test, deciding which failures matter and coordinating a cutover without using production as the test environment.
If your team needs someone to map those dependencies and run the technical and operational work together, Greg can help plan and manage the Ubuntu 26.04 rollout.
Related on GrN.dk
- NGINX 1.30 changed upstream connection reuse by default: what to check before you upgrade
- Apache 2.4.67 Put Legacy Reverse Proxies Back on the Risk List
- Apache 2.4.68 Is a Reminder That Old Proxy Rules Need a Real Audit
Need help with this kind of work?
Plan a safer Ubuntu 26.04 rollout Get in touch with Greg.